Diamond
Claim Your ConnectSecure Powered CyberCert Credits.
You already find and fix vulnerabilities across your clients. ConnectSecure turns that work into certification outcomes, giving MSPs and providers one platform to see the risk, close it, and prove it, from the SMB on the tools right through to the enterprise managing them in their supply chain. Exploiting known, unpatched vulnerabilities is now the number one way attackers break in. ConnectSecure is how you shut that door, and evidence it against the standard.
To qualify:
Start your ConnectSecure free trial and deploy it within your MSP to scan, prioritize and patch your own environment. This earns you a sponsored CyberCert Certification Credit for your own business.
Roll ConnectSecure out across your CyberCert programs of work and onboard SMB clients onto the platform. Every client you assess and secure with ConnectSecure earns you another sponsored Certification Credit.
Apply to get started.
Fill out the form today to apply for your Sponsored Credits, powered by ConnectSecure. Add any questions in the comments too!
Powered by
Credits fund CyberCert certification subscriptions and do not guarantee certification, which is earned through independent assessment by CyberCert. Conditions apply for sponsored credits. ConnectSecure finds, prioritises and helps remediate vulnerabilities and maps them to the standard; full certification at each tier also requires controls ConnectSecure does not itself provide, such as the firewall, antivirus, endpoint detection and response, multi-factor authentication and staff training. ConnectSecure pairs with the rest of your stack to complete a tier.
Why ConnectSecure
+ CyberCert.
Delivering CyberCert certification across a client portfolio isn't hard because the standard is complex. The harder part is proving it, showing, asset by asset, that the known holes are found, fixed, and staying fixed. That is exactly what most SMBs can't see for themselves, and exactly what ConnectSecure was built to do.
ConnectSecure is the visibility and proof underneath the standard.
Attackers rarely need a zero-day. They walk through known vulnerabilities that already have a patch, and they favour the assets no one is watching. ConnectSecure maintains a live connection to the NIST National Vulnerability Database, tracking over 230,000 known vulnerabilities, maps them to your clients' assets, and ranks them by EPSS, real-world exploitation probability, not just theoretical severity. So you fix what actually matters first, and you can show the work.
And SMB1001 is built right in.
ConnectSecure includes SMB1001 as a built-in compliance framework, alongside the Essential Eight and more than fifteen others. That means you can assess a client directly against the standard, see the gaps, close them with automated remediation, and generate the audit-ready evidence, all from one platform, all white-labelled as you. Every scan moves a client closer to certification, and you earn a sponsored credit while you do it.
One platform. Every environment. Every client.
For MSPs and providers, this creates a genuinely scalable delivery engine:
- Scan everything from one console: internal networks, the external attack surface, Active Directory, firewalls, PII, Microsoft 365, Google Workspace and web applications
- Complete asset discovery that uncovers even unknown and shadow IT assets
- EPSS-based prioritisation that ranks vulnerabilities by what's actually being exploited
- Patch 360 automates patching for 1,850+ third-party applications, plus OS updates, with verification
- SMB1001 and 15+ frameworks built in, with continuous compliance monitoring
- White-labelled, audit-ready reporting for auditors, insurers and boards
- Multi-tenant management across your whole book
What's Included?
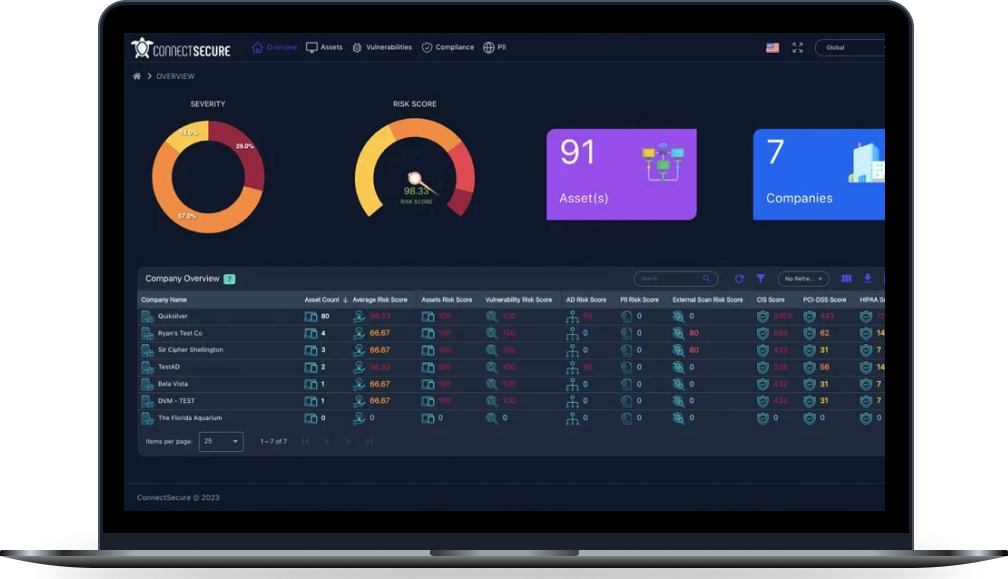
The ConnectSecure platform, purpose-built for MSPs to find, prioritise, fix and evidence vulnerabilities across every client environment.
A sponsored CyberCert Certification Credit for every client you onboard and secure with ConnectSecure.
Internal, external, cloud, Microsoft 365, Google Workspace and web application scanning, plus Active Directory, firewall and PII scans.
Live NIST NVD intelligence tracking 230,000+ known vulnerabilities, mapped to client assets.
EPSS prioritisation that ranks vulnerabilities by real-world exploitation probability.
Automated remediation and patching with Patch 360 for 1,850+ third-party applications, plus OS updates.
SMB1001 as a built-in compliance framework, with gap assessment and continuous monitoring.
White-labelled, audit-ready compliance and vulnerability reporting.
Multi-tenant management for your whole client base.
A free trial for your MSP, earning your first sponsored CyberCert Certification Credit.
The bigger picture.
Enterprise clients are increasingly requiring their SMB suppliers to hold cyber certifications. But most SMBs can't see their own vulnerabilities, let alone prove they're managing them, and most MSPs haven't had a clean way to turn the scanning and patching they already do into certification outcomes at scale.
ConnectSecure and CyberCert close both gaps. The MSP runs the rollout. ConnectSecure finds the risk, fixes it, and maps it to the standard. CyberCert provides the independent certification. And the enterprise gets real, verifiable evidence that their supply chain is cyber secure.